Security Assessment for Digital Products
We analyze your digital product from an attacker's point of view before an attacker does. In a structured workshop we work out the threats with your team, rate them by risk and derive concrete measures, straight into your architecture and backlog.
The Challenge
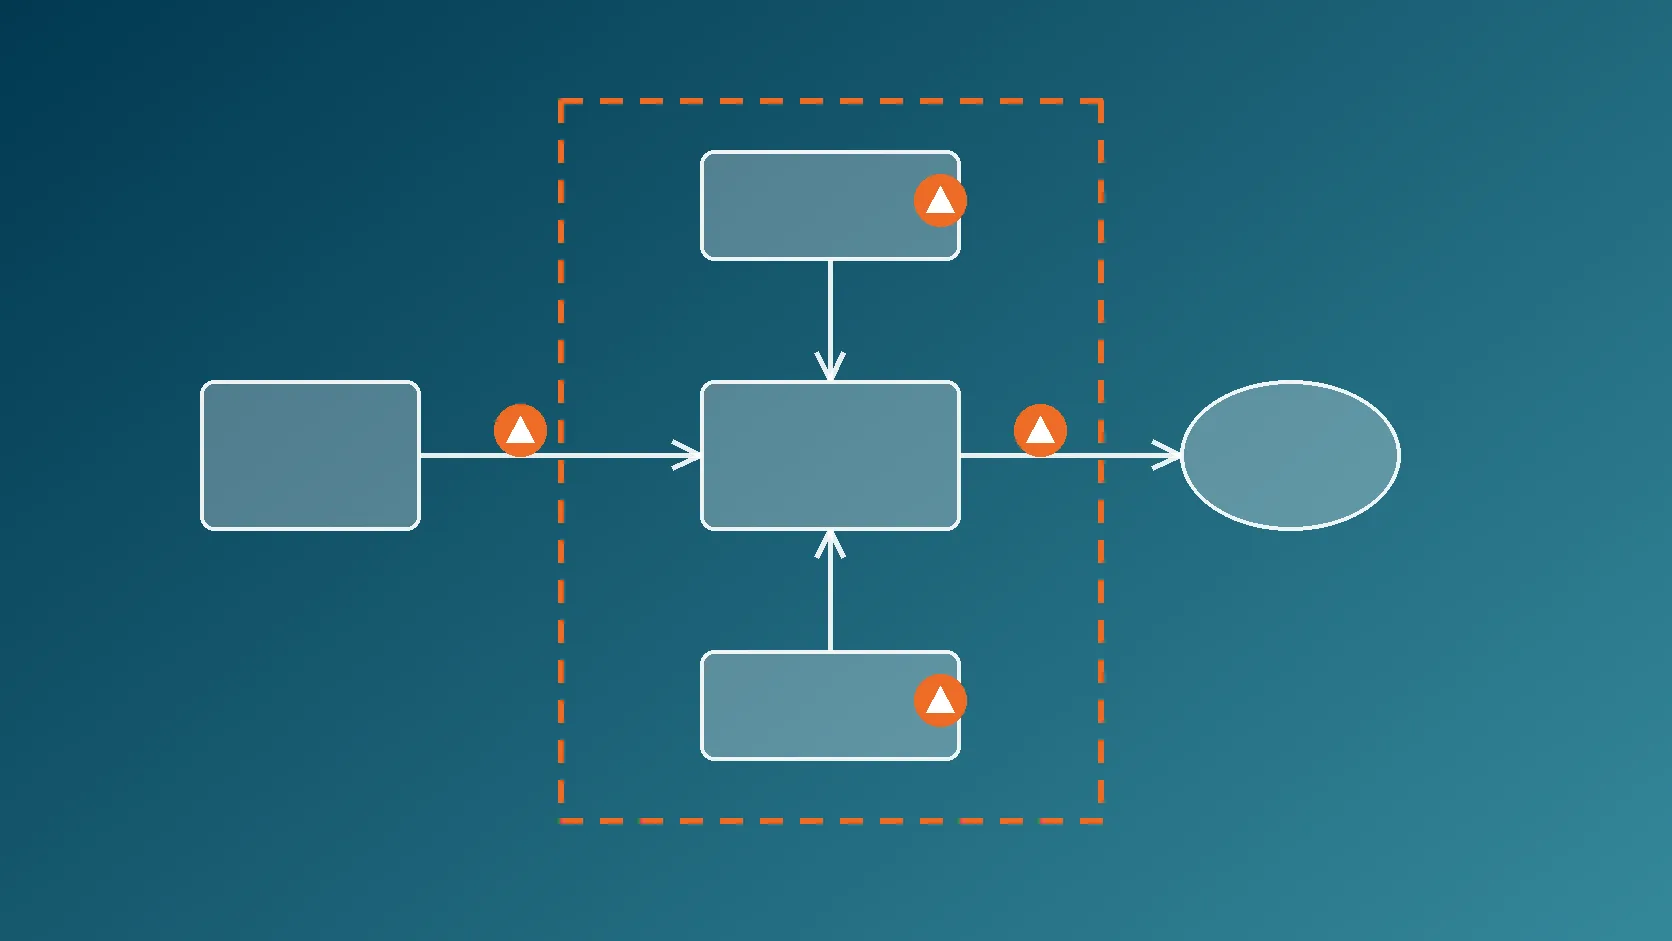
Security cannot be bolted onto a product afterwards. If the architecture is designed without a threat analysis, weaknesses arise exactly where they are most expensive to fix later: trust boundaries, interfaces and data flows. With the Cyber Resilience Act, manufacturers must also demonstrate a risk assessment of their product. Many teams know they need threat modeling, but lack the method, the experience and a neutral outside view.
What a security assessment covers
Threat modeling
Systematic threat analysis of your product architecture, e.g. with STRIDE: data flows, trust boundaries, attack surface.
Security by design
Security requirements and architecture principles that flow into design and development from the start.
Risk rating & prioritization
Threats rated by likelihood and impact, so your team tackles the most important ones first.
Embedded & connected devices
For products with hardware: threat analysis based on MITRE EMB3D, tailored to your device class.
Measures for backlog & architecture
Concrete, actionable countermeasures your team can take straight into architecture decisions and tickets.
Evidence for the CRA & more
Documented results as a building block of your risk assessment and technical documentation under the CRA.
The workshop offer: threat modeling workshop
A focused workshop with your development and architecture team. We facilitate, bring the method and deliver a robust result.
Preparation
We clarify scope, product and architecture documents and agree on the participants.
Workshop (1 to 2 days)
Model data flows and trust boundaries together, identify threats with STRIDE, complemented by MITRE EMB3D for hardware products.
Assessment
Risk rating and prioritization of the identified threats.
Result report
Documented threat model with prioritized measures, ready for your backlog and CRA documentation.
Review workshop
We come back and review together which findings have been implemented in the meantime and what remains open.
See what the result looks like
Download a sample security assessment report and see how findings, risks and measures are documented.
Download the test report ↓Learn threat modeling yourself
Prefer to build the skills in your own team? The EACG Academy offers our courses on the topic.
Threat Modeling
From architecture to countermeasure: method, STRIDE and a fully worked practical example.
To the course →MITRE EMB3D
Threat modeling for embedded and connected devices using the EMB3D knowledge model.
To the course →MITRE ATT&CK
Understand real-world adversary techniques and rate threats realistically.
To the course →